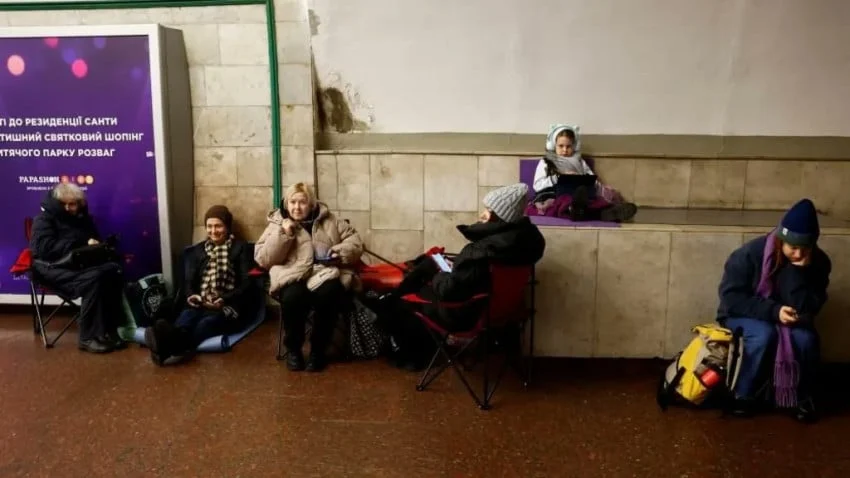
In a bizarre and alarming turn of events amid the ongoing war, both Ukraine and Russia experienced a coordinated or simultaneous cyberattack targeting their national air-raid warning systems. On a tense Sunday evening, millions of citizens across the geopolitical divide received terrifying, yet entirely false, notifications warning of imminent nuclear strikes, chemical hazards, and urban street combat. The unprecedented digital intrusion highlights the profound vulnerabilities embedded within critical civil defense infrastructure, raising urgent questions regarding the expanding scope of modern electronic warfare and the growing threat of psychological operations conducted via state-of-the-art mobile applications.
The digital breach affected the primary civilian warning mechanisms utilized to alert populations of incoming aerial threats. While citizens in both warring nations are accustomed to frequent alerts regarding conventional missile and drone bombardments, the introduction of catastrophic scenarios—specifically nuclear and chemical contamination warnings—triggered widespread panic and forced national cybersecurity agencies to scramble damage control measures. As investigators sift through the digital wreckage, the incident has underscored the terrifying potential for hostile actors to weaponize civilian information channels, turning tools designed for life-saving protection into vectors for psychological warfare.
Main Facts of the Sunday Cyber Incident
The cyber incident unfolded in rapid succession across the international border. In Ukraine, the widely utilized "Air Alarm" application—downloaded by millions of citizens and integrated deeply into daily life since the escalation of the full-scale invasion in February 2022—suddenly flashed emergency warnings of the highest severity. The notifications did not merely signal standard aerial bombardments; they explicitly warned of widespread radiation leaks, chemical weapons deployment, and active ground combat in metropolitan centers, including the capital city of Kyiv.
Just hours later, authorities across the border in the Russian Federation reported a strikingly similar digital compromise. Russian state-affiliated channels and regional civil defense networks confirmed that mobile applications mirroring Ukraine’s warning system had been successfully breached. In the Russian cases, the false alerts were laced with explicit language, profane insults, and alarming tactical warnings designed to destabilize public trust and create administrative chaos.
Despite the high-stakes nature of the breach, preliminary investigations by independent cybersecurity analysts indicate that the hackers did not compromise the underlying infrastructural architecture of national military radar systems, but rather targeted the software application programming interfaces (APIs) or content management systems utilized by third-party software developers to push notifications to end-users. Nevertheless, the psychological impact was immediate, leaving millions grappling with the terrifying prospect of an apocalyptic escalation.
Chronology of the Breach and Immediate Response
The timeline of Sunday’s events demonstrates a high degree of digital coordination, though whether a single sophisticated threat actor, rival state-sponsored hacker collectives, or disgruntled insiders were responsible remains under active investigation.
Late Sunday Afternoon: The first anomalies were detected as routine notification channels experienced uncharacteristic latency. Within minutes, the Ukrainian "Air Alarm" application initiated a nationwide level-red alert override. Unlike standard notifications which are drafted in Ukrainian, the unauthorized messages disseminated to users were composed in the Russian language. This linguistic anomaly served as an immediate red flag for seasoned users, many of whom quickly recognized that the syntax and terminology did not align with official state emergency broadcast standards.
Early Sunday Evening: Panic began to trend across social media platforms as bewildered citizens sought clarification. Recognizing the systemic breach, the Ukrainian Air Force took to official communication channels, publishing an urgent bulletin via Telegram. The military command explicitly stated: "Aplikasi Air Alarm mungkin telah menjadi sasaran gangguan musuh. Tidak ada ancaman radiasi! Tetap tenang dan ikuti pembaruan kami di saluran kami." (The Air Alarm application may have been targeted by enemy interference. There is no radiation threat! Stay calm and follow our updates on our channel.)
Mid-Sunday Evening: Ukrainian software developers, operating in tandem with state cybersecurity units, initiated a mandatory emergency shutdown of the application’s notification gateway. The government announced that the platform was being temporarily taken offline for comprehensive diagnostic maintenance, confirming publicly that the software had been "apparently compromised."
Late Sunday Night: As Ukrainian systems were being brought back under control, reports emerged from the Russian Federation indicating that regional civil defense and mobile warning applications had suffered an identical fate. Unauthorized messages, some containing vulgarities and mocking commentary regarding state leadership, were pushed to thousands of mobile devices. Russian emergency services scrambled to issue manual retractions through television broadcasts and official state media channels, urging the populace to disregard the rogue smartphone notifications.
Broader Context: The Evolution of Digital Warfare
The simultaneous compromise of civil defense apps in both countries illustrates a fundamental shift in contemporary military strategy. For decades, electronic warfare was strictly confined to the electromagnetic spectrum—jamming radar, spoofing GPS signals, and disrupting military command-and-control networks. However, the ongoing conflict has accelerated the convergence of conventional warfare with large-scale cyber operations targeting the civilian rear-guard.
In Ukraine, mobile applications have become an indispensable part of daily existence. The "Air Alarm" app, developed in cooperation with the Ministry of Digital Transformation and tech firms like Stfalcon, functions as a digital lifeline. It utilizes data feeds from military radar installations to provide localized warnings down to the district level, affording citizens crucial minutes to seek shelter before Russian hypersonic missiles or loitering munitions strike. By subverting this system, the perpetrators of Sunday’s attack struck directly at the psychological resilience of the Ukrainian civilian population, attempting to induce fatigue, despair, and distrust in state institutions.
Conversely, the breach of Russian warning systems highlights vulnerabilities within the Russian domestic digital landscape. While the Russian state exercises stringent control over national internet infrastructure (often referred to as the "RuNet"), regional administrative digital systems frequently rely on outsourced software contractors, leaving them exposed to sophisticated penetration testing and remote exploitation by advanced persistent threat (APT) groups.
Official Responses and Institutional Assessments
In the wake of the incident, cybersecurity agencies in Kyiv and Moscow offered divergent narratives while sharing a common objective: restoring public confidence in national security infrastructure.
Ukrainian officials emphasized the psychological motivations behind the attack. Representatives from the Ministry of Digital Transformation noted that the use of the Russian language in the fraudulent alerts was a deliberate tactical error by the perpetrators, which ultimately mitigated the scale of the panic by signaling to users that the messages were fraudulent. Officials reaffirmed their commitment to hardening software supply chains and implementing multi-factor authentication protocols for all administrative accounts capable of pushing push notifications.
In Moscow, state media downplayed the technical severity of the breach, framing it as a crude provocation orchestrated by hostile foreign intelligence agencies seeking to sow internal discord. Russian emergency ministries stressed that physical civil defense sirens—the traditional network of acoustic alarms deployed across major cities—remained entirely unaffected by the cyber intrusion, proving that critical infrastructure was distinct from commercial mobile applications.
Cybersecurity experts observing the conflict have pointed out that the incident underscores the inherent risks of relying on centralized, cloud-based applications for emergency broadcasting. When millions of smartphones are tethered to a single software pipeline, any compromise of administrative credentials instantly transforms a public utility into a weapon of mass deception.
Implications and Future Risks for Global Security
The dual cyberattack on Ukrainian and Russian warning systems carries profound implications not only for the immediate combatants but for global cybersecurity architecture at large. As artificial intelligence and automated exploitation tools become increasingly accessible to state-sponsored and non-state actors alike, the integrity of civilian infrastructure worldwide faces unprecedented threats.
-
The Weaponization of Information Fatigue: Prolonged exposure to conflict breeds psychological exhaustion. Incidents like the Sunday breach are designed to exploit this fatigue, making populations more susceptible to panic, misinformation, and fatalistic resignation. When citizens can no longer trust their emergency alerts, the threshold for effective disaster response is severely compromised.
-
Software Supply Chain Vulnerabilities: Both incidents demonstrate that modern civil defense is heavily dependent on commercial software development ecosystems. Third-party vendors, outsourced coding teams, and cloud-hosted database management systems represent soft targets for sophisticated hackers seeking asymmetric impacts without engaging in direct kinetic combat.
-
The Escalation of Cyber Deterrence: The blurring lines between military command networks and civilian mobile infrastructure complicate the doctrine of cyber deterrence. If an attack on a civilian weather or warning application can be construed as an act of psychological warfare or state-sponsored sabotage, it raises difficult questions regarding appropriate retaliatory thresholds under international law.
As technical teams in both countries work to patch vulnerabilities and audit their software source codes, Sunday’s unprecedented event serves as a sobering reminder that the battlefield of the 21st century extends far beyond trenches and artillery batteries. In an era where smartphones serve as both shields and early warning systems, the digital frontier remains fiercely contested, with the civilian populace standing directly in the crosshairs of invisible digital warfare.